
Blog
What is DDoS Protection
What DDoS protection is and how NoFlare DDoS Protector keeps your business online — real-time detection, gigabit-level protection, BGP routing, iptables filtering and reverse proxies.
Oct 20, 2025 · NoFlare Team
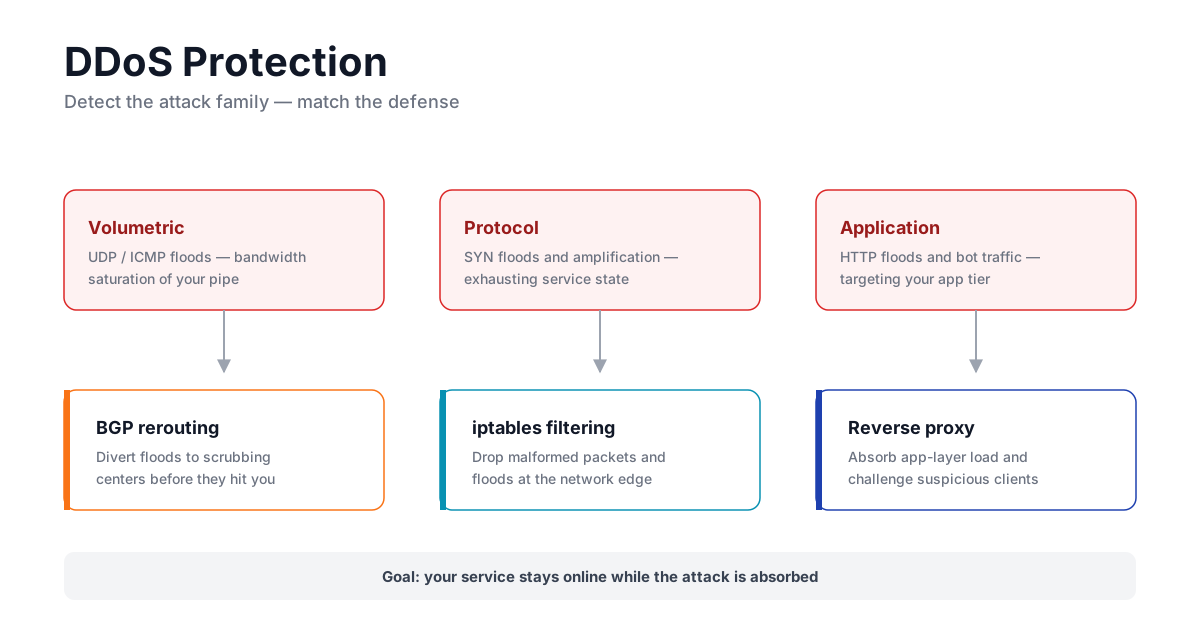
Distributed Denial of Service (DDoS) protection is the set of controls that keep your services available when attackers try to overwhelm them with traffic. Done well, it protects your revenue, your customers' access and your reputation — not just your network.
Why DDoS protection matters
DDoS attacks are among the most common and damaging threats a business faces. Whether you are a small team or a large enterprise, an attack can interrupt service, cost revenue and damage your reputation. DDoS protection is how you stop that from happening.
The cost math is straightforward. An attack during a sales campaign, a product launch or a month-end run does not just cost the hours your team spends responding — it costs the transactions that did not happen, the customers who switched to a competitor that was online, and the support load of explaining the outage afterwards. For many organizations, one serious attack in a year exceeds the annual cost of continuous protection. DDoS protection is one of the few security investments whose absence is directly visible to your customers.
What a DDoS attack looks like
Most DDoS attacks fall into three broad families, and each one exploits a different weakness:
- Volumetric attacks flood your network with more traffic than your links can carry — the classic "overwhelm the pipe" attack.
- Protocol attacks abuse the rules of network protocols to exhaust resources on your infrastructure, such as connection tables and session memory.
- Application-layer attacks send requests that look legitimate, so they slip past simple volume thresholds while your servers spend their capacity serving them.
From the business side, the distinction matters because it determines what protection you actually need. Stopping a volumetric flood is a capacity and routing problem; stopping an application-layer attack is a detection and filtering problem. Effective DDoS protection addresses all three.
What NoFlare DDoS Protector does
NoFlare provides enterprise-grade protection across the techniques that actually stop attacks.
Real-time detection and mitigation
NoFlare identifies DDoS traffic in real time and begins mitigation the moment an attack is detected, so your team is not racing the attacker. Detection is continuous and traffic-based, which means the platform reacts to what is actually happening on your network rather than to a pre-written list of signatures.
Gigabit-level protection capacity
NoFlare is engineered to absorb high-volume attacks — the kind that would saturate a small business's uplink in seconds. Protection capacity is part of the platform from the start, so you are not paying for an entry-tier product that stops working at the moment a real attack arrives.
BGP routing integration
NoFlare integrates with BGP to reroute malicious traffic away from your servers, so legitimate traffic flows smoothly while attack traffic is filtered before it reaches your infrastructure. Rerouting at the network layer is what makes large volumetric attacks survivable: the traffic is handled where it can be handled, not at your fragile edge.
Iptables firewall integration
NoFlare uses customizable iptables rules to block malicious IPs and filter harmful traffic at the network level, tailored to your environment without disrupting legitimate users. The rules are specific to the attack, so legitimate customers keep working while the malicious sources are cut off.
Reverse proxy protection
NoFlare's reverse proxy hides your web servers' real IP addresses, preventing direct targeting and letting only legitimate users reach your services. Hiding the origin is a durable control: even after an attack ends, your infrastructure is harder to find and harder to hit directly next time.
Seamless integration with minimal latency
NoFlare integrates with your existing infrastructure and adds protection without noticeable latency, so your users are not affected. Availability protection that makes the site slower defeats its own purpose; NoFlare is tuned so the protected path is as fast as the unprotected one.
Why businesses choose NoFlare
- Business continuity — services stay online even under aggressive attacks.
- Scalability — protection that fits small businesses and large enterprises.
- Cost-effective security — prevents the downtime, lost revenue and recovery costs that follow an attack.
- 24/7 monitoring and support — our security team monitors your network and helps you respond to threats.
Stay secure with NoFlare
DDoS attacks are becoming more frequent and more sophisticated, and reliable defense is essential to maintaining business continuity. NoFlare DDoS Protector gives you multi-layered, real-time protection against all types of DDoS attacks, so your network, your reputation and your bottom line stay protected.
Contact us to learn how NoFlare can keep your network safe from DDoS threats.